
 by
Introduction
In 2025, cyber threats have evolved beyond traditional hacking attempts. Modern enterprises operate in complex environments involving multi-cloud platforms, remote employees, IoT devices, APIs, and AI-driven systems. This massive digital expansion has made traditional perimeter-based security models ineffective.
Attackers no longer “break the wall” — they log in using stolen credentials, compromised devices, or misconfigured cloud services.
This is why enterprises worldwide are shifting to Zero Trust Security Architecture (ZTSA), a model built on one powerful principle:
“Never trust, always verify.”
Zero Trust is now considered the foundation of modern cybersecurity strategies for governments, banks, healthcare systems, and global enterprises.
What is Zero Trust Security Architecture?
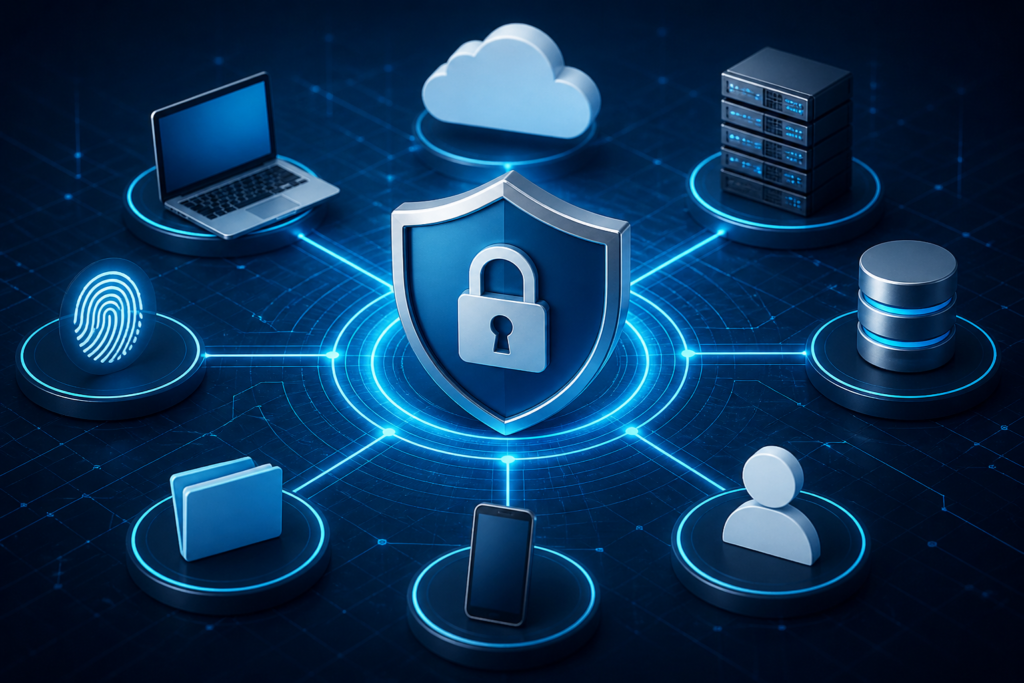
Zero Trust Security Architecture (ZTSA) is a cybersecurity framework that assumes:
- No user is trusted automatically
- No device is trusted by default
- No network location is inherently safe
Instead, every access request is continuously verified using identity, context, and risk-based policies.
According to modern cybersecurity standards like NIST, Zero Trust is designed for cloud-first, hybrid, and distributed systems, where traditional security boundaries no longer exist.
Why Traditional Security Models Fail
Traditional cybersecurity worked on a simple idea:
“If you are inside the network, you are trusted.”
But in 2025, this model fails because:
1. Remote Work Explosion
Employees access systems from home, coffee shops, and mobile devices.
2. Cloud Infrastructure
Data is no longer inside a single data center.
3. Credential Theft
Stolen passwords are the #1 attack vector.
4. Insider Threats
Even authorized users can cause damage intentionally or accidentally.
Advanced strategies for preventing internal breaches are covered under Insider Threat Detection.
5. API & AI Systems
Machines now communicate with machines, increasing attack surfaces.
Core Principles of Zero Trust Architecture
The foundation of Zero Trust Security Architecture is based on strict identity verification.
1. Never Trust, Always Verify
Every request must be authenticated and authorized before access.
2. Least Privilege Access
Users only get the minimum required permissions to perform tasks.
3. Assume Breach
Security systems are designed as if attackers are already inside.
4. Continuous Verification
Authentication is not one-time — it is ongoing.
5. Identity-Centric Security
Identity becomes the new security perimeter.
A strong identity-based approach is essential, which is explained in detail under Identity and Access Management (IAM).
Core Components of Zero Trust Architecture
Core elements of Zero Trust Security Architecture include identity and access control systems.
1. Identity and Access Management (IAM)
IAM ensures that only verified users can access systems using:
- Multi-Factor Authentication (MFA)
- Single Sign-On (SSO)
- Role-Based Access Control (RBAC)
2. Zero Trust Network Access (ZTNA)
ZTNA replaces VPNs with secure, identity-based access to applications.
Instead of giving full network access, users get:
- App-level access only
- Session-based authentication
- Continuous verification
3. Microsegmentation
Networks are divided into small isolated zones.
So even if an attacker enters:
- They cannot move freely
- Damage remains limited
4. Security Policy Engine
This system evaluates:
- User identity
- Device health
- Location
- Behavior patterns
- Risk score
5. Continuous Monitoring
AI-powered tools detect:
- Suspicious login patterns
- Data exfiltration attempts
- Abnormal behavior
How Zero Trust Works in Real Enterprises
A simple Zero Trust workflow:
- User tries to access a system
- Identity is verified (MFA + credentials)
- Device is checked for security compliance
- Behavior risk is analyzed
- Access is granted only to specific resources
- Session is continuously monitored
- Any abnormal activity triggers instant restriction
This ensures that even if attackers steal credentials, they cannot freely access the system.
Benefits of Zero Trust Security Architecture
1. Strong Breach Prevention
Even if attackers enter, they cannot move across systems.
2. Reduced Attack Surface
Only necessary resources are exposed.
3. Better Cloud Security
Works seamlessly across AWS, Azure, and hybrid systems.
4. Protection Against Insider Threats
Limits damage from compromised internal accounts.
5. Faster Threat Detection
AI-based monitoring identifies threats in real time.
6. Compliance Support
Helps meet:
- GDPR
- ISO 27001
- NIST standards
Recommended Video: Zero Trust Security Architecture Explained
Challenges in Implementing Zero Trust
1. Legacy Systems
Old infrastructure is difficult to upgrade.
2. High Complexity
Requires redesign of enterprise architecture.
3. Cost of Tools
IAM, SIEM, ZTNA tools require investment.
4. Skill Gap
Requires trained cybersecurity professionals.
5. User Experience Issues
Frequent authentication may slow workflows.
Future of Zero Trust
The evolution of Zero Trust Security Architecture is shaping enterprise cybersecurity.
1. AI-Driven Security
AI will automatically adjust access permissions in real time.
2. Identity for Everything
Not just users — even devices, APIs, and AI agents will have identities.
3. Fully Perimeterless Networks
Traditional network boundaries will disappear completely.
4. Behavioral Authentication
Passwords will be replaced with behavior-based verification.
5. Zero Trust for AI Systems
Even AI models will require strict access control.
Real-World Importance
Zero Trust is now used in:
- Banking systems (fraud prevention)
- Healthcare (patient data protection)
- Government infrastructure (national security)
- Cloud providers (AWS, Azure security models)
- Enterprises (enterprise-wide access control)
Conclusion
Zero Trust Security Architecture in 2025 is not just a cybersecurity trend — it is a fundamental shift in how enterprises protect digital assets.
By eliminating implicit trust and enforcing continuous verification, organizations can defend against modern threats like:
- Credential theft
- Cloud misconfigurations
- Insider attacks
- AI-driven cyber threats
In today’s digital-first world, Zero Trust is no longer optional — it is a critical enterprise security requirement.

One thought on “Zero Trust Security Architecture in 2025 for Critical Enterprise Protection”